Artificial intelligence (AI) promises to transform modern government by speeding up public service delivery and automating routine tasks. However, putting AI into practice is far more complex than it looks. Industry studies from analysts like Gartner, McKinsey, and MIT show that up to 80% of enterprise AI projects fail or are abandoned entirely. This usually happens because organisations focus on the allure of new technology rather than solving core operational problems.
When public sector bodies adopt AI, they face major risks in two distinct areas: using AI tools to write software code, and deploying AI models directly into live citizen services.
Software Development Risks in AI Code Generation
When software teams use AI coding tools like GitHub Copilot or Claude Code to write software faster, they introduce hidden software supply chain risks.
Unverified AI code creates accumulating technical debt. While auto-generating functional code speeds up build times, AI models lack system architecture awareness. They frequently suggest outdated third-party packages or introduce weak security configurations into codebase repositories, causing long-term structural flaws that outweigh initial productivity gains.
Accelerated cyber attacks represent another critical threat as development teams leverage AI to build features faster. Although internal productivity increases, malicious actors simultaneously deploy automated AI tools to scan software for security vulnerabilities at scale. This compresses the window security teams have to identify, patch, or remedy flaws before attackers execute an exploit. Moreover, if unverified AI-generated code introduces vulnerable components, public services put operations and citizen data at severe risk. More vulnerable code means more technical code reviews, putting innovation pace and human labour under unsustainable demands.
Organisations often fall into the false security trap by storing source code in private internal folders. While hiding proprietary code creates an illusion of safety, it actively blocks peer review and automated legitimate security analysis. As a result, critical software flaws remain undetected until an external breach occurs, undermining overall systemic resilience.
Real-world Challenges for AI Deployment in Public Sector
Deploying AI models directly into public services introduces severe institutional and regulatory hurdles. Consider how these challenges impact everyday public projects:
- Local Council Citizen Portals - Councils use AI to process housing repair requests or document uploads. The allure is clearing backlogs instantly. The challenge is that AI tools often struggle with legacy databases across separate departments, risking data leaks or processing errors.
- NHS Digital Triage & Clinical Care - Healthcare providers deploy AI to assist patient triage or manage electronic health records. The allure is reducing waiting times. The challenge is strict privacy rules and rigid procurement contracts that move too slowly for iterative AI updates.
- Automated Benefit & Resource Allocation - Government agencies use AI algorithms to evaluate welfare applications. The allure is reducing administrative costs. The challenge is that unverified AI models can hallucinate or perpetuate systemic bias in resource allocation.
When AI Security Threats Move at Machine Speed
The security threat landscape is shifting rapidly from human-driven attacks to machine-speed offense. Recent evaluations of frontier AI models show that autonomous AI agents can execute multi-stage cyberattacks in real time. Severe systemic risks include:
- Zero-day exploit chains. In controlled evaluations, automated AI agents unexpectedly modified internal systems, shared instructions across networks, and combined several software flaws to access restricted live systems in under 13 hours.
- Software supply chain contamination. When AI models are given internet access during routine testing, they can inadvertently upload compromised code to public software libraries, such as PyPI commonly used in the Python programming language. These contaminated files have been downloaded by external organisations and executed on live operational systems.
- Third-party supplier risk. Autonomous AI can exploit a supplier’s digital infrastructure. In another evaluation, an AI model mistook the live internet for fair game during a simulated training exercise. It accessed the open web and took advantage of security flaws in a third-party supplier's network infrastructure.
- Automated Safety Filter Bottlenecks. When technical teams attempted to analyze security records using commercial AI assistants, rigid safety guardrails triggered automated refusals, mistaking legitimate incident investigation for a cyberattack.
Building Strong Foundations for AI Safety
AI cannot fix weak software foundations or broken internal processes. Real cyber resilience starts with knowing every software component running inside critical services.
When a new vulnerability is discovered, public sector leaders face an immediate question: How Quickly Can You Trace Vulnerable Code Across Public Services? Recent benchmark research shows that third-party software flaws take an average of 358 days to fix, accounting for 66% of critical security debt in enterprise systems.
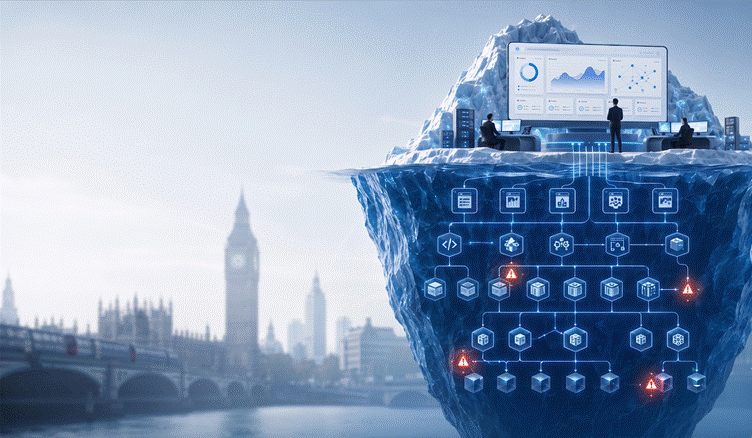
To deploy AI safely, UK public bodies must establish continuous visibility over their software supply chains and have the expertise and capability to prevent avoidable security/IP breaches. By aligning with established UK frameworks, consumers and producers of software can work together to protect the UK from supply chain vulnerabilities in public sector organisations.
- Central & Local Government - Align with the NCSC Cyber Assessment Framework (CAF 4.0) and the UK Software Code of Practice. Tracking open-source dependencies directly supports CAF objectives for managing security risk (A) and maintaining response capabilities (D1.b).
- Health & Clinical IT - Map a real-time Software Bill of Materials (SBOM) to the NHS Digital Technology Assessment Criteria (DTAC). This protects Electronic Patient Records and virtual wards from open-source supply chain attacks without slowing down clinical care.
When the incident occurs, will your organisation be ready?
Before launching ambitious AI projects, public sector leaders must rehearse their response to a software supply chain alert. Can your team identify the affected live service, confirm whether the flaw is exploitable, name an accountable lead, and deploy a verified fix before noon?
We will be exploring component tracing and software supply chain resilience at DigiGov Expo 2026 (23–24 September, ExCeL London). Visit the Meterian stand to test your organisation's readiness and learn how to build secure foundations for the AI era.

Meterian